Cyber Security Analyst: No Degree? What Australian MSPs Check Instead
An Australian MSP explains what junior cyber security analysts need to get hired, from IT experience and certifications to practical skills and lab work.
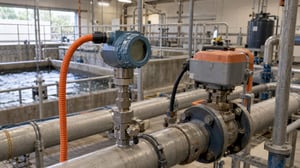
ICS Security for SMBs: What Your MSP Should Fix First
Learn how industrial control systems work, why safety shapes ICS security, and which practical steps SMBs and MSPs can prioritize without disrupting…
Australian Cyber Security Degrees: What Makes Graduates Hireable
See how cyber security degrees in Australia compare on course levels, practical labs, employer expectations, SME roles, entry requirements, and career value.
OT Security Best Practices for Australian SMBs: From ASD to Action
Apply ASD and IEC 62443 guidance to OT security: inventory assets, segment networks, secure vendor access, and test ransomware resistant backups for SMBs.
MSP Tested Security Awareness Best Practices for Australian SMEs
MSP-tested, practical security awareness for Australian SMEs: continuous microlearning, quarterly phishing simulations, mandatory MFA and tested backups…
Security Incident Management for 10–50 Staff: MSP 90 Day Playbook
MSP tested plan to build a security incident management system for 10–50 staff SMBs: practical trade offs, 30, 60 and 90 day milestones, and backup and…
MFA + restore test stop 3 information security threats for Australian SMBs
Australian SMBs: identify the three biggest information security threats, phishing and ransomware, human error, and stolen credentials, and take two first…
48 Hour Rule: Vulnerability Management Lifecycle for Brisbane SMBs
Lifecycle guide to finding and prioritising vulnerabilities, with the ASD/ACSC 48 hour patch rule and MSP fixes tailored for Brisbane SMBs.
Stop Breaches: 30, 90 and 180 Day Cyber Security Mitigation Techniques for SMBs
MSP-tested cyber security mitigation techniques for SMBs: 30, 90 and 180 day priorities to fix MFA, backups, patching, EDR, and admin rights.